ComAct360 by Re-Infotech
ComAct360 turns India’s Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 into everyday workflows: versioned privacy notices, a tamper-evident consent ledger, rights requests with deadlines, breach clocks for CERT-In and the Data Protection Board, ROPA, vendors, retention and a cookie banner. It keeps the evidence an auditor, a customer or the Board will ask for.

ComAct360 is DPDP compliance software built by Re-Infotech in Ponda, Goa, for any business that collects personal data of people in India. It gives your Data Protection Officer, legal, IT and HR teams one place to run the programme and prove it: who consented to what and under which notice, which rights requests are open and how long is left, which breach reports are due, which vendors process your data and under what contract, and what must be erased and when.
Why now: the DPDP Rules, 2025 were notified on 13 November 2025. The Consent Manager rules apply from 13 November 2026, and most duties for businesses (notice, security safeguards, breach intimation, retention, children’s data and rights of Data Principals) apply from 13 May 2027. Penalties under the Act go up to ₹250 crore for failing to take reasonable security safeguards and ₹200 crore for failing to report a breach.
New to the law? Read our DPDP Act compliance guide for Indian businesses.

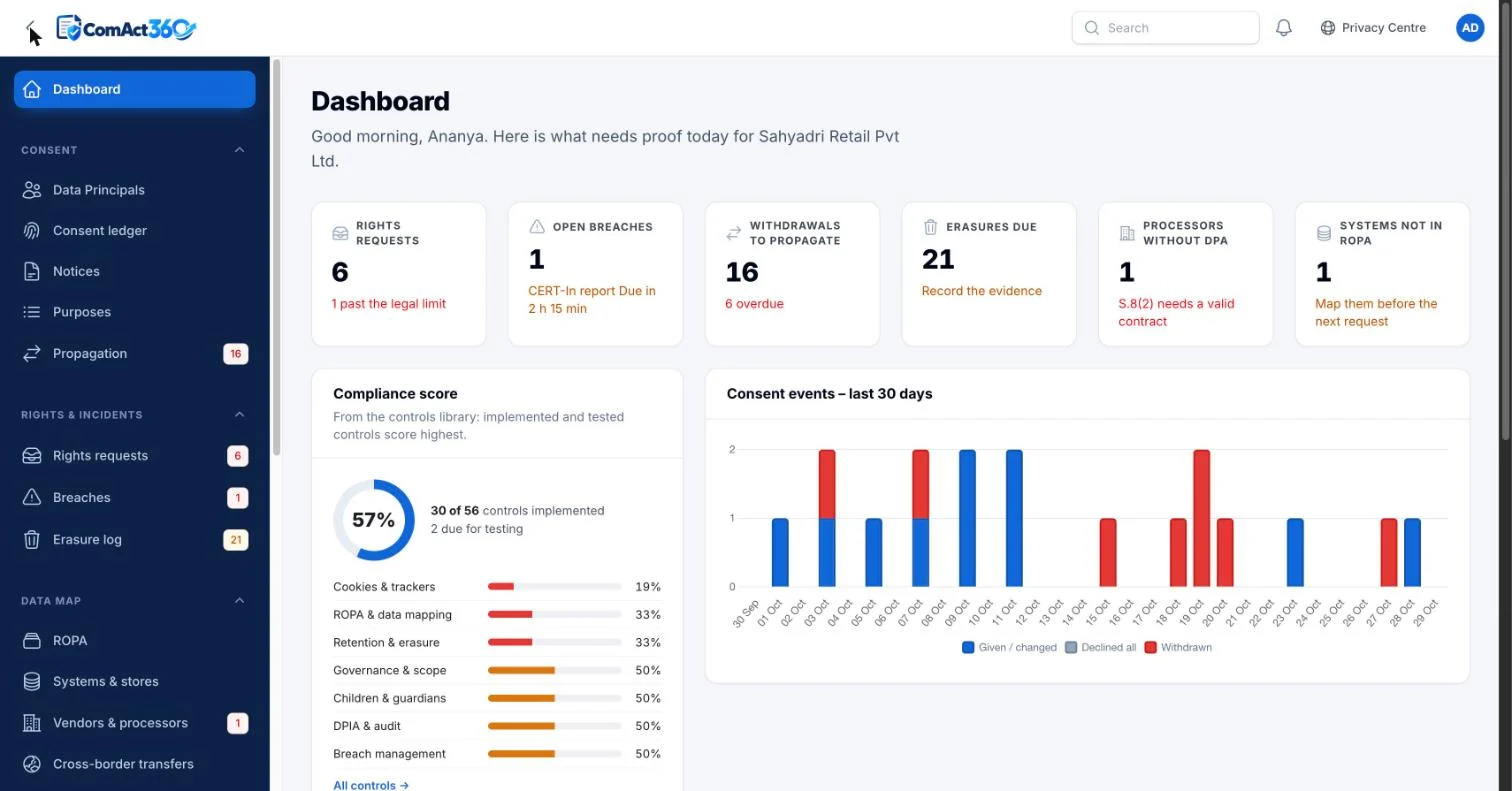
The ComAct360 dashboard: open rights requests, breach clocks, withdrawals to pass on, erasures due, processors without a contract and your compliance score. Screenshot with sample data.

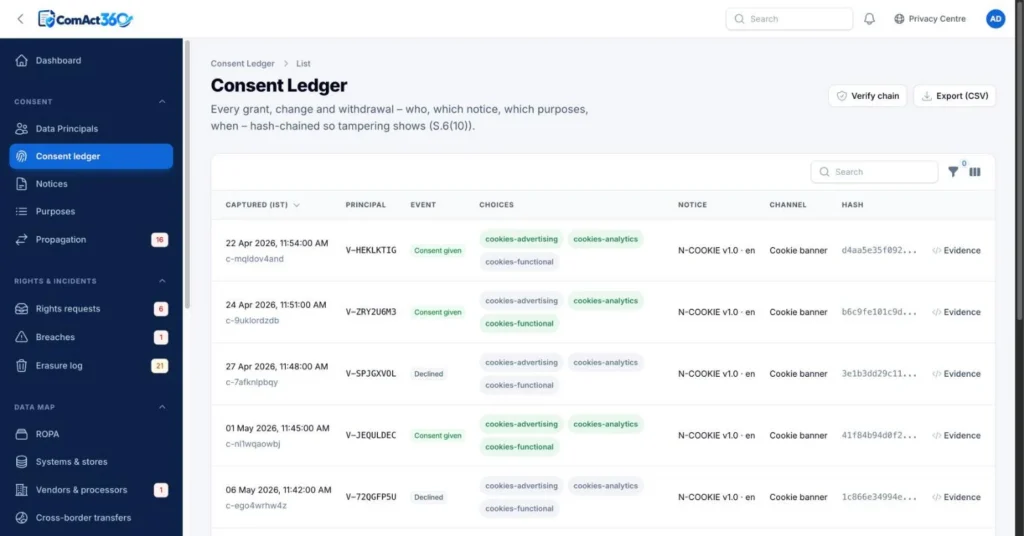
ComAct360 consent ledger recording every consent given, changed or withdrawn with notice version, purposes, channel and a hash chain.
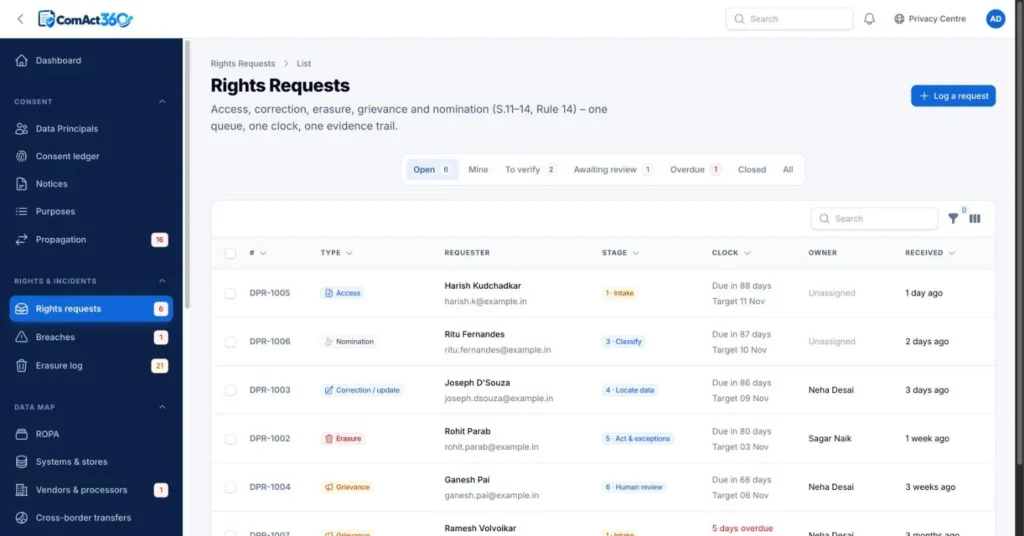
ComAct360 rights requests queue for access, correction, erasure, grievance and nomination requests with stage, owner and deadline.
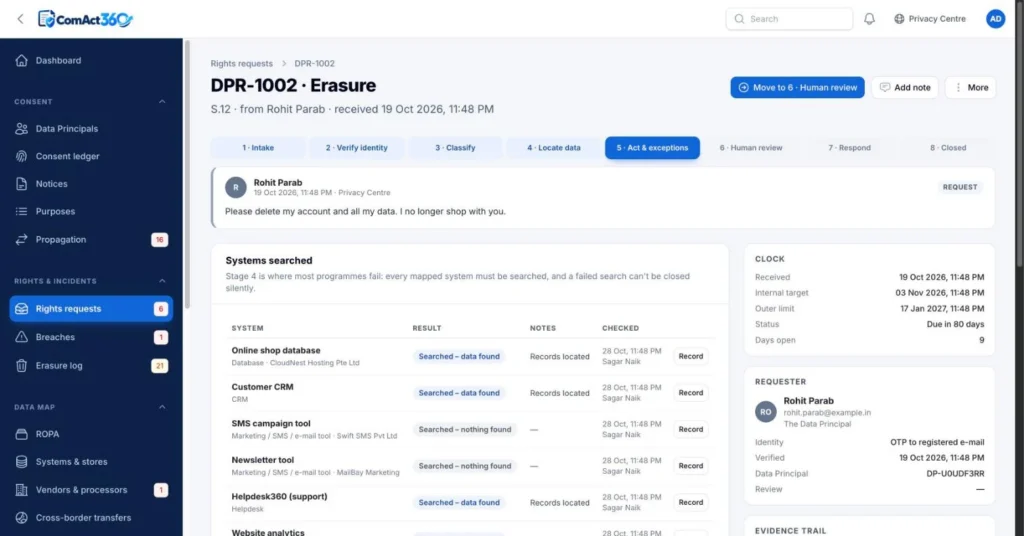
ComAct360 erasure request moving through 8 stages, with every mapped system searched and recorded before closing.
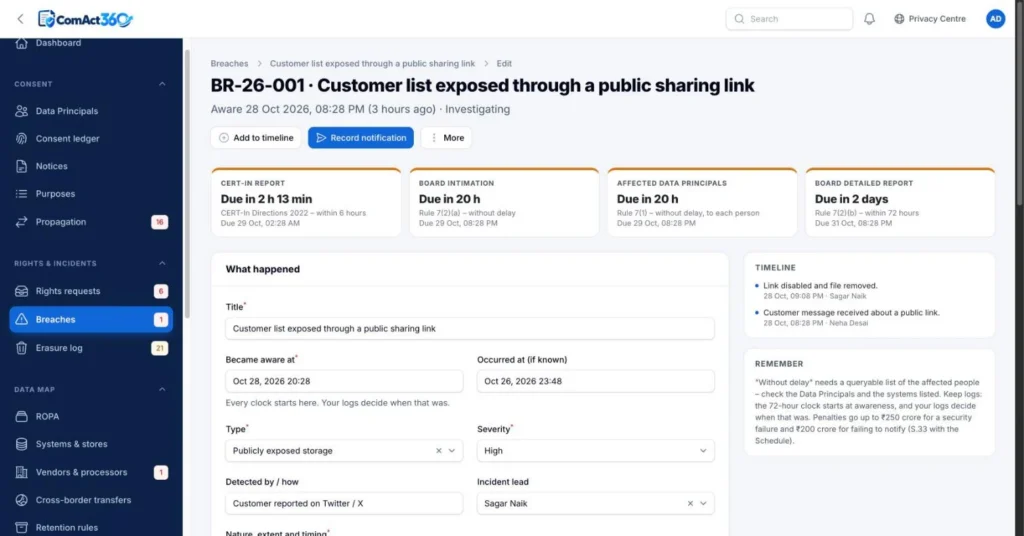
ComAct360 breach record with live clocks for the CERT-In 6-hour report, Board intimation, affected people and the Board's 72-hour detailed report.
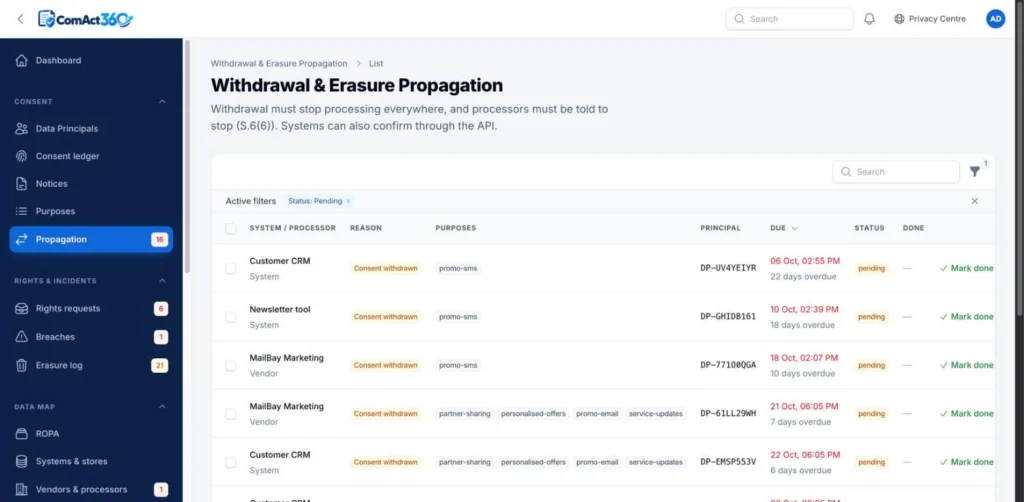
ComAct360 propagation tasks telling every system and processor to stop processing after a consent withdrawal, with due dates.
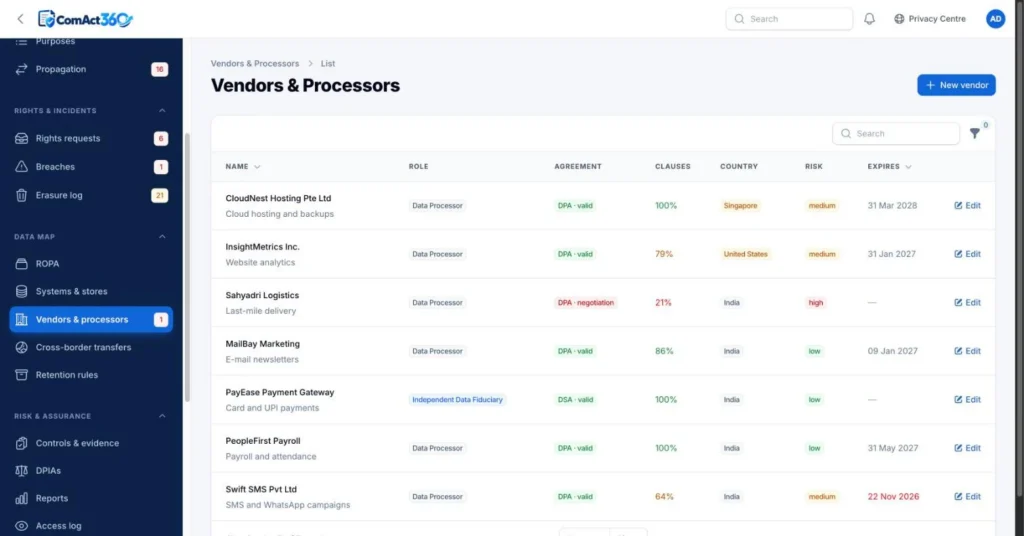
ComAct360 vendor and processor register with agreement status, DPA clause score, country, risk rating and expiry.
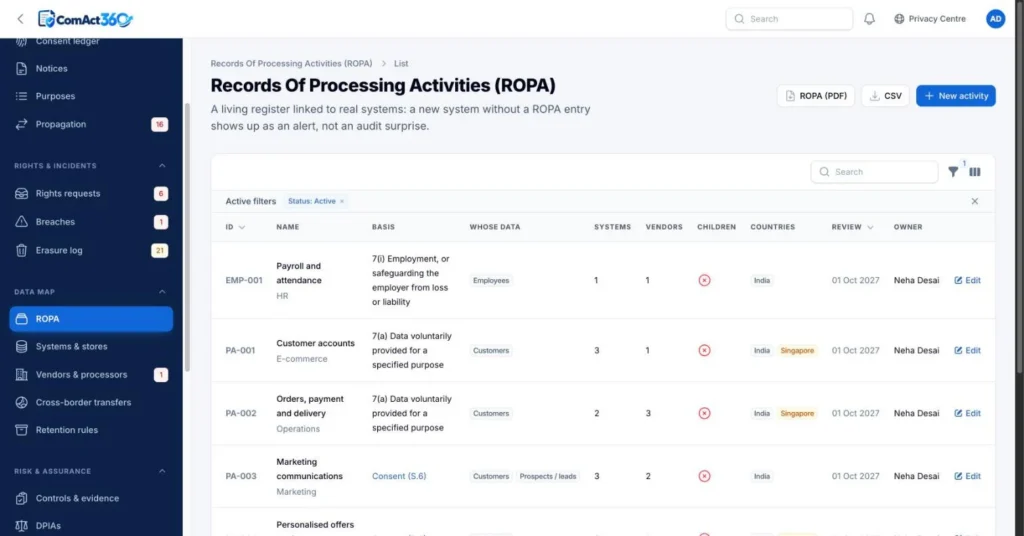
ComAct360 records of processing activities (ROPA) with legal basis, whose data, systems, vendors, children flag and countries.
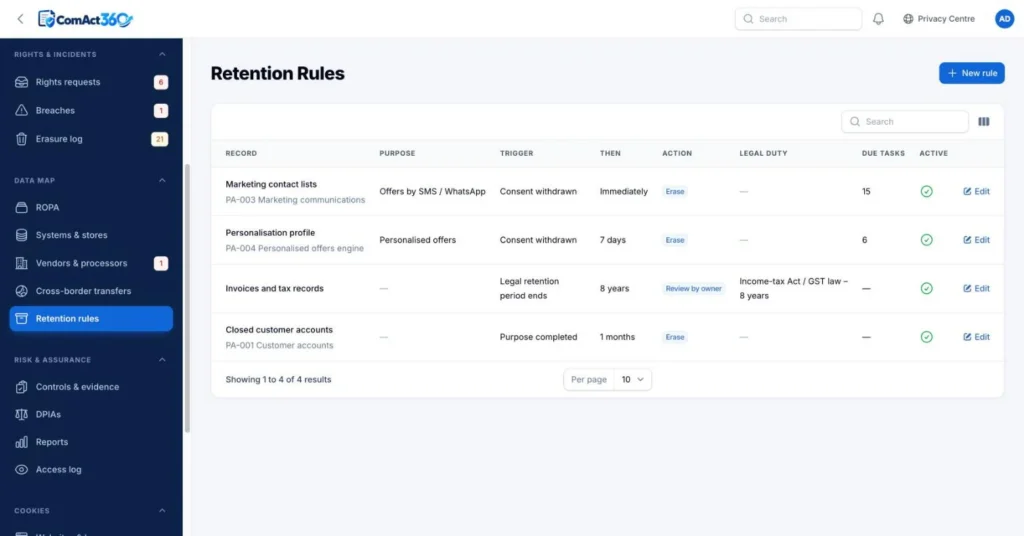
ComAct360 retention rules: what to erase, when and why, including legal retention duties.
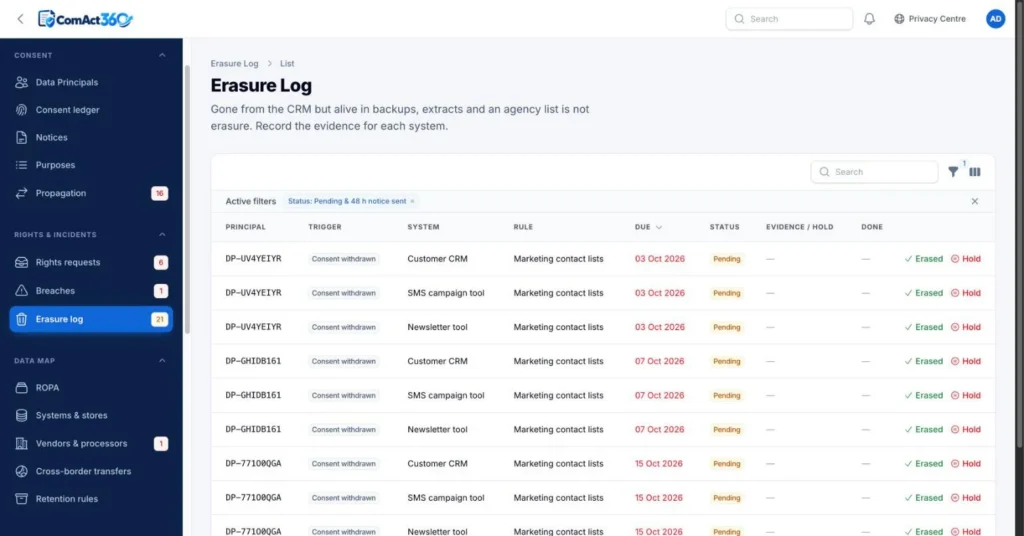
ComAct360 erasure log listing data to erase from each system after consent withdrawal, with due dates and evidence.
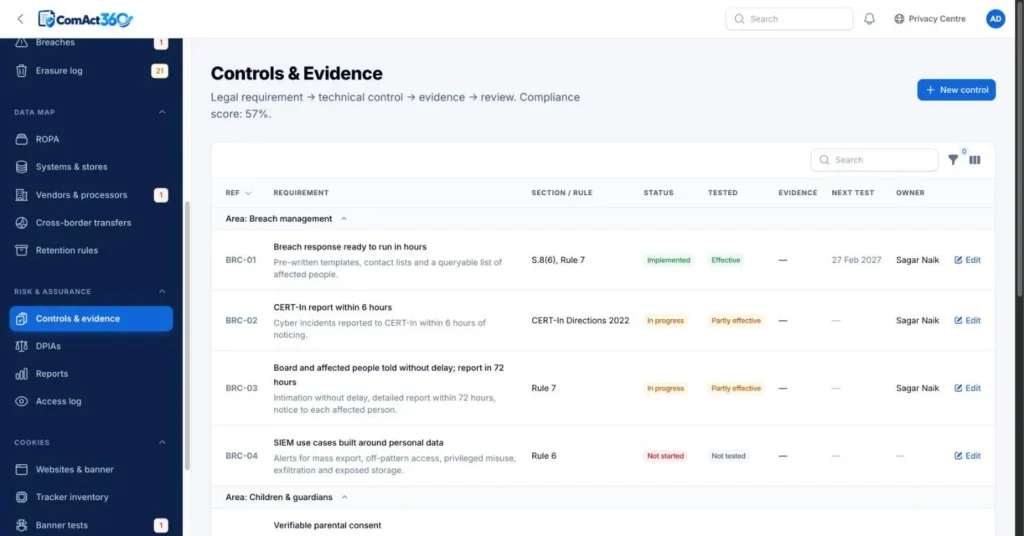
ComAct360 controls library linking each DPDP requirement to a control, test status, evidence and owner.
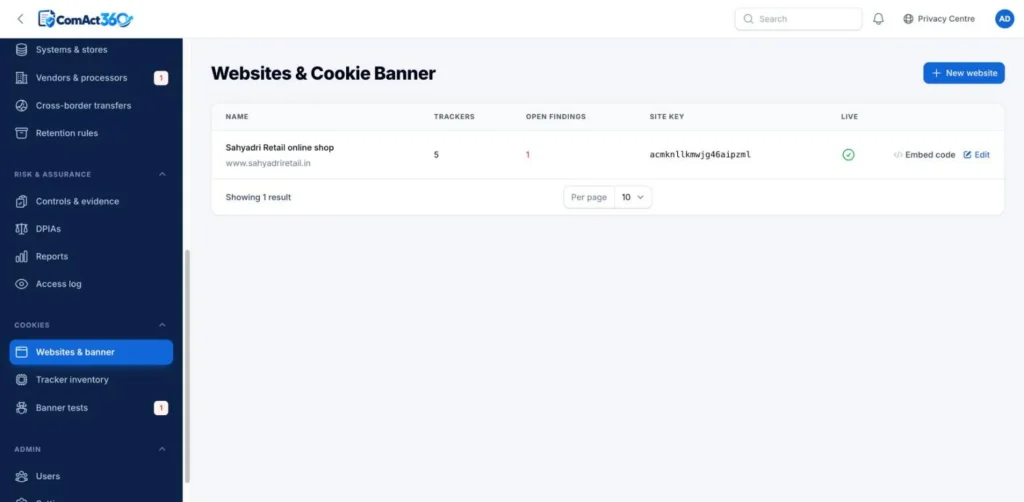
ComAct360 websites and cookie banner setup with tracker count, banner test findings and embed code.
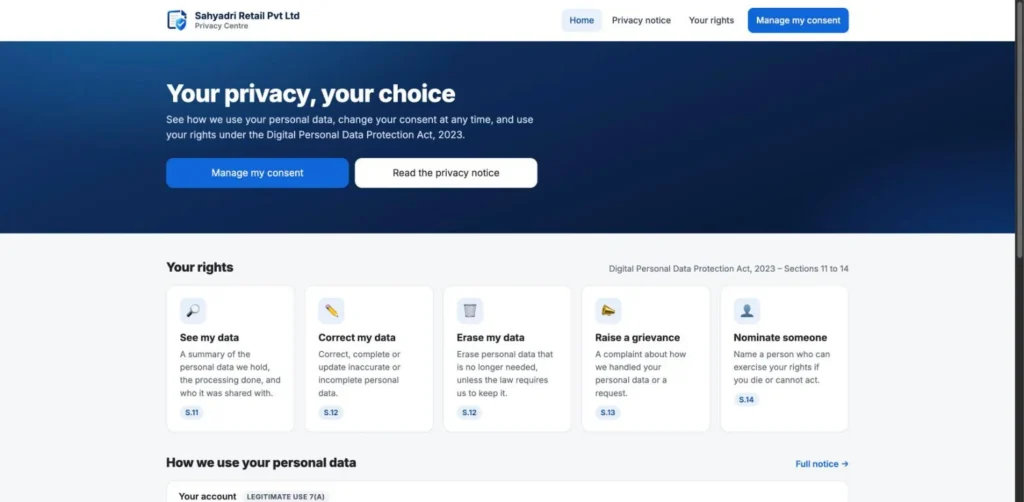
ComAct360 Privacy Centre where customers manage consent, read the notice and use their DPDP rights to access, correct, erase, complain and nominate.
Screenshots from the live ComAct360 app with sample data.
How it works
We list your systems, vendors and purposes with you and build your record of processing (ROPA).
Your privacy notice, Privacy Centre and cookie banner go live, in English and Indian languages.
Your team handles consent, rights requests, withdrawals and breaches from one screen, with deadlines.
Every action leaves evidence: consent records, search logs, breach notices, erasure logs and control tests.
Who it’s for
ComAct360 suits any organisation in India that collects customer, patient, student or employee data, especially where there are many systems, vendors or children’s data. It is used by DPOs, legal and compliance teams, IT and HR, with a read-only seat for auditors.
Features
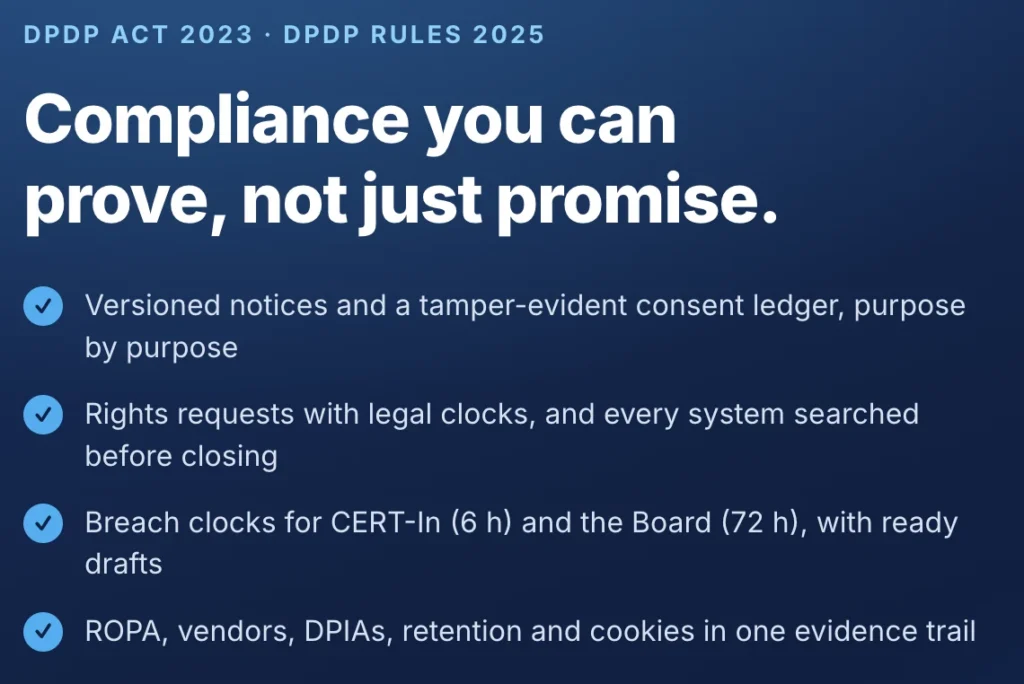
Purpose-by-purpose choices, versioned notices in English and Indian languages, and a hash-chained consent ledger. Withdrawal takes one tap (S.5, S.6).
Access, correction, erasure, grievance and nomination requests move through 8 stages, with every system searched and DPO review before replying (S.11–14).
Live countdowns for the CERT-In 6-hour report, Board intimation, affected people and the 72-hour detailed report, with draft notices (Rule 7).
Verifiable parental consent, child-safe defaults and no tracking or targeted ads for under-18s (S.9, Rules 10–11).
ROPA, systems, processors with contract checklists, cross-border transfers, retention rules and an erasure log (S.8, S.16, Rule 8).
A default-deny cookie banner for your website, and an API so your CRM, SMS and e-mail tools check consent before they send.
Every duty in the DPDP Act and Rules has a place in ComAct360, and a proof.
| The law asks | Section / Rule | ComAct360 gives you |
|---|---|---|
| Notice | S.5, Rule 3 | Versioned, multi-language notices, locked once published with a digital fingerprint |
| Consent | S.6 | One choice per purpose, a tamper-evident ledger, consent on any past date, an evidence PDF |
| Withdrawal | S.6(4), 6(6) | One tap to withdraw; every system and processor gets a task to stop, tracked until confirmed |
| Children | S.9 | Restricted mode, verified parent or guardian, no tracking or targeted ads for under-18s |
| Rights | S.11–14 | An 8-stage request pipeline with deadlines, system-by-system search and DPO approval |
| Processors | S.8(2) | Vendor register with a contract clause checklist, expiry alerts and risk ratings |
| Breaches | S.8(6), Rule 7 | Parallel clocks for CERT-In, the Board and affected people, with draft notices |
| Retention | Rule 8 | Retention rules, 48-hour notices before erasure, and an erasure log with evidence |
FAQ
ComAct360 is DPDP Act compliance software by Re-Infotech, Goa. It manages privacy notices, consent, rights requests, breaches, ROPA, vendors, retention and cookie consent for businesses in India, and keeps the evidence of each step.
The DPDP Rules, 2025 were notified on 13 November 2025. Consent Manager provisions apply from 13 November 2026, and most obligations for businesses (notice, security safeguards, breach intimation, retention, children’s data and rights of Data Principals) apply from 13 May 2027.
Under Rule 7, the Data Protection Board and each affected person must be told without delay, and the Board must get a detailed report within 72 hours of becoming aware, unless it allows longer. Separately, CERT-In’s 2022 Directions require cyber incidents to be reported within 6 hours. ComAct360 runs all these clocks in parallel.
Every consent given, changed or withdrawn is recorded with the person, the notice version, each purpose, the channel and the time. Records are hash-chained so tampering shows, and you can export the evidence for any person or date.
Yes. ComAct360 gives you a cookie banner embed code for your website, a consent API your CRM and messaging tools can check before sending, and withdrawal tasks for every system and processor that must stop.
No. ComAct360 is software to run your DPDP programme and keep evidence. Your legal adviser or DPO decides the legal positions; Re-Infotech helps you set up the software, notices and workflows.
Tell us a little about your organisation and we will call you back to arrange a free demo of ComAct360.
2nd Floor, Ponda Commerce Centre, SO-15, Tiska, Durgabhat, Ponda, Goa 403401
Monday to Saturday, 10 am to 6 pm
enquiry@re-infotech.com
We call or WhatsApp you during working hours, Monday to Saturday, 10 am to 6 pm.
A short conversation about your business, goals and current setup.
Clear recommendations, scope and a fixed quote, with no obligation.
Your details are used only to respond to your enquiry. See our Privacy Notice.